Case study · Own product
Eurtifact: evidence for what is in every release
An EU-sovereign platform that quarantines, scans, SBOMs and signs open-source container images before they reach a team. Every step is recorded in an audit trail that NIS2 and CRA auditors can verify.
01 · The problem
Open source without evidence has become a risk.
EU software manufacturers build on thousands of upstream components. These often arrive through registries outside the EU, without recorded evidence of what was pulled, scanned and deployed.
Since 11 September 2026, manufacturers under the Cyber Resilience Act must report actively exploited vulnerabilities (Article 14), and Annex I requires a machine-readable SBOM with every product. Their customers under NIS2 ask the same questions in supplier questionnaires.
Existing approaches were fragmented: ad-hoc mirrors, manual scans and compliance evidence in spreadsheets. Eurtifact replaces that with one controlled path.
02 · Architecture
The digital customs house.
Every artifact follows the same controlled path, from untrusted source to verified distribution.
- 01
Upstream sources
Monitors public registries (Docker Hub, GHCR, Quay) for images on the allowlist. New versions and tags are detected automatically.
- 02
Quarantine & mirror
Each artifact lands in an isolated quarantine project. Nothing is available to tenants until inspection is complete.
- 03
Scan & certify
Scan for known CVEs, CycloneDX SBOM, Cosign signature. Each step is recorded as a lifecycle event.
- 04
Policy gate
Per-tenant admission policies decide what is promoted. The platform enforces data completeness; each organisation sets its own thresholds.
- 05
Secure distribution
Approved artifacts go to tenant registries within the EU. Every pull is logged, from source to deployment.
03 · Engineering decisions
Six decisions that shape the design.
- 01
Quarantine first
A new artifact is unreachable by default. Release is an explicit step after inspection, not an exception after the fact.
- 02
Allowlist instead of an open proxy
Only images on the allowlist are mirrored. That limits the attack surface and makes the origin of every component traceable.
- 03
Policy per tenant
The platform guards data completeness; each organisation sets its own release thresholds.
- 04
Hash-chained audit trail
Every action goes into an immutable, chained log. Compliance becomes provable, not self-declared.
- 05
Everything inside the EU
Compute, storage and backups run at Hetzner in Germany. Artifact data, metadata and audit logs do not leave the EU.
- 06
Open standards
CycloneDX for SBOMs, Cosign for signatures and CNCF components. No proprietary formats that lock a customer in.
04 · Security and regulation
Controls, mapped to the law.
Mapping to NIS2 and the CRA
| Article | Requirement | Platform control |
|---|---|---|
| NIS2 Art. 21(2)(d) | Supply chain security | Allowlist-based curation, upstream provenance recorded |
| NIS2 Art. 21(2)(e) | Secure development | Quarantine-scan-certify pipeline, immutable build records |
| NIS2 Art. 21(2)(h) | Cryptography | Cosign, TLS 1.3, AES-256 |
| CRA Annex I, Part II(1) | Machine-readable SBOM | CycloneDX for every artifact version |
| CRA Annex I, Part II(7) | Secure update distribution | Signed distribution to tenant registries |
| CRA Art. 14 | Reporting to CSIRT/ENISA | Structured incident workflow with configurable timelines |
Security controls
- TLS 1.3 in transit, AES-256 at rest
- Cosign signatures on every released artifact
- Isolated tenant with its own policies and audit trail
- Pseudonymised audit logs, no personal data in artifact processing
- Coordinated disclosure via security.txt (RFC 9116)
- Every pull logged
05 · Status
Live, and open to inspect.
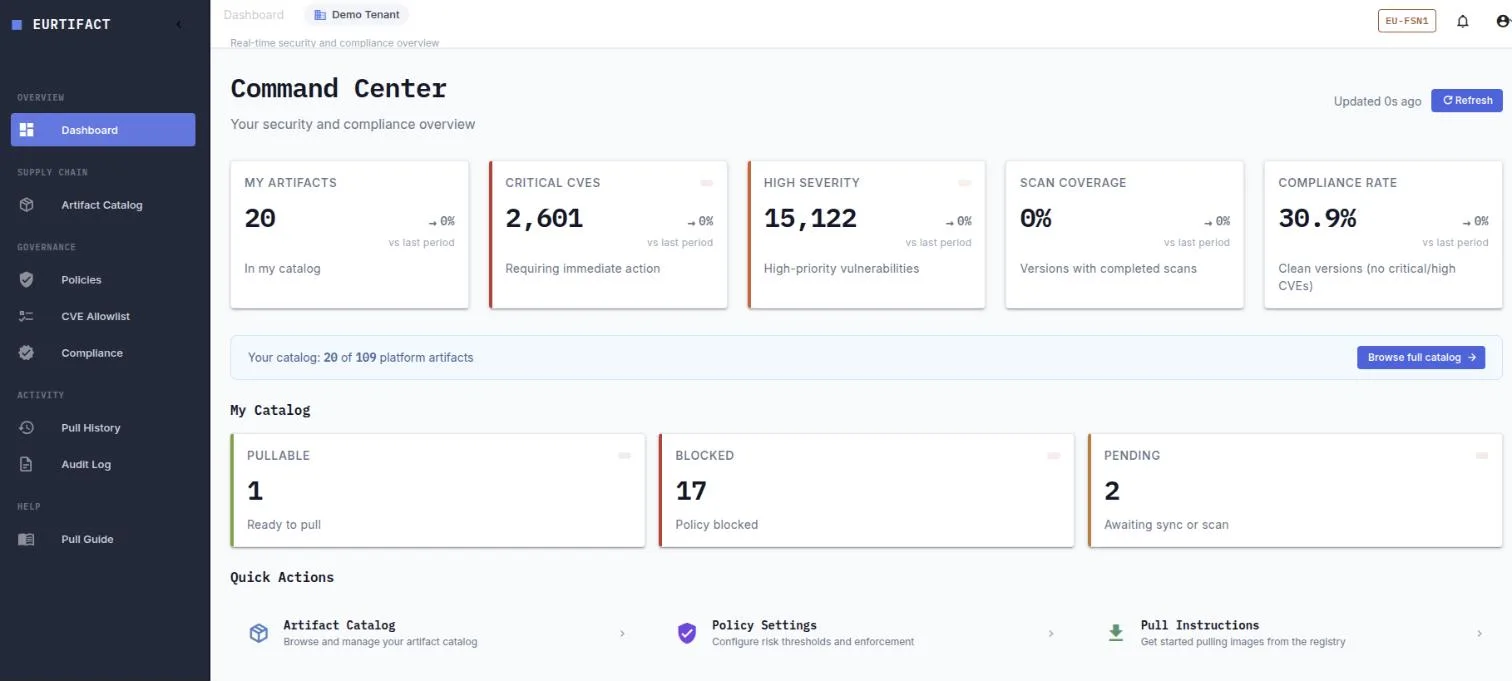
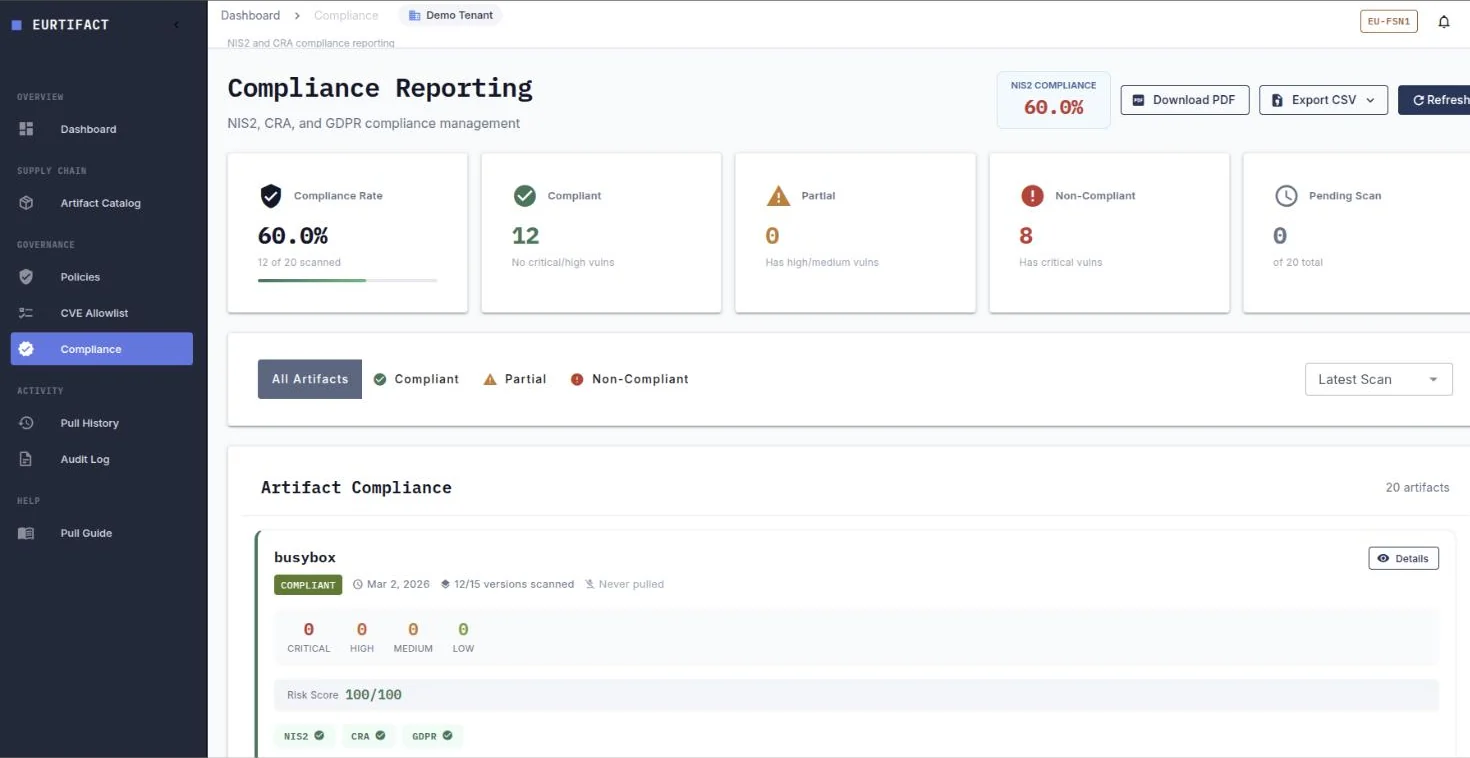
The platform runs in production in Germany. eurtifact.eu has a live demo with real screens from a tenant. Eurtifact is aimed at EU software manufacturers that fall under the CRA and have customers under NIS2.
Eurtifact is a product of Yildiz Tech, the company behind Poolster Solutions. The mapping to legal articles describes technical controls; it is not a legal declaration of conformity.
eurtifact.euNeed an audit trail for your own supply chain?
We help you choose between Eurtifact and a setup in your own cloud, built on the same principles.